
This article contains affiliate links. If you buy through them, MyrinNew.com may earn a commission at no extra cost to you.
🕒 4 min read
An AI system that can read a document is different from one that can publish a message, change a record, or spend money. Before giving an assistant access to business tools, evaluate the actions the surrounding software permits. A reassuring instruction in a prompt is not an access-control system.
The following review framework focuses on the boundary between untrusted content and authorized actions. It can be used for a proposed integration before a pilot or when an existing assistant receives a new connector.
Draw the action boundary
List the tools and the precise operations available through each. Separate read access from writes, and writes from irreversible consequences. “Access to WordPress” is not specific enough: reading published posts, editing drafts, changing users, and publishing externally are different capabilities.
Affiliate pick: tech accessories
Belkin US
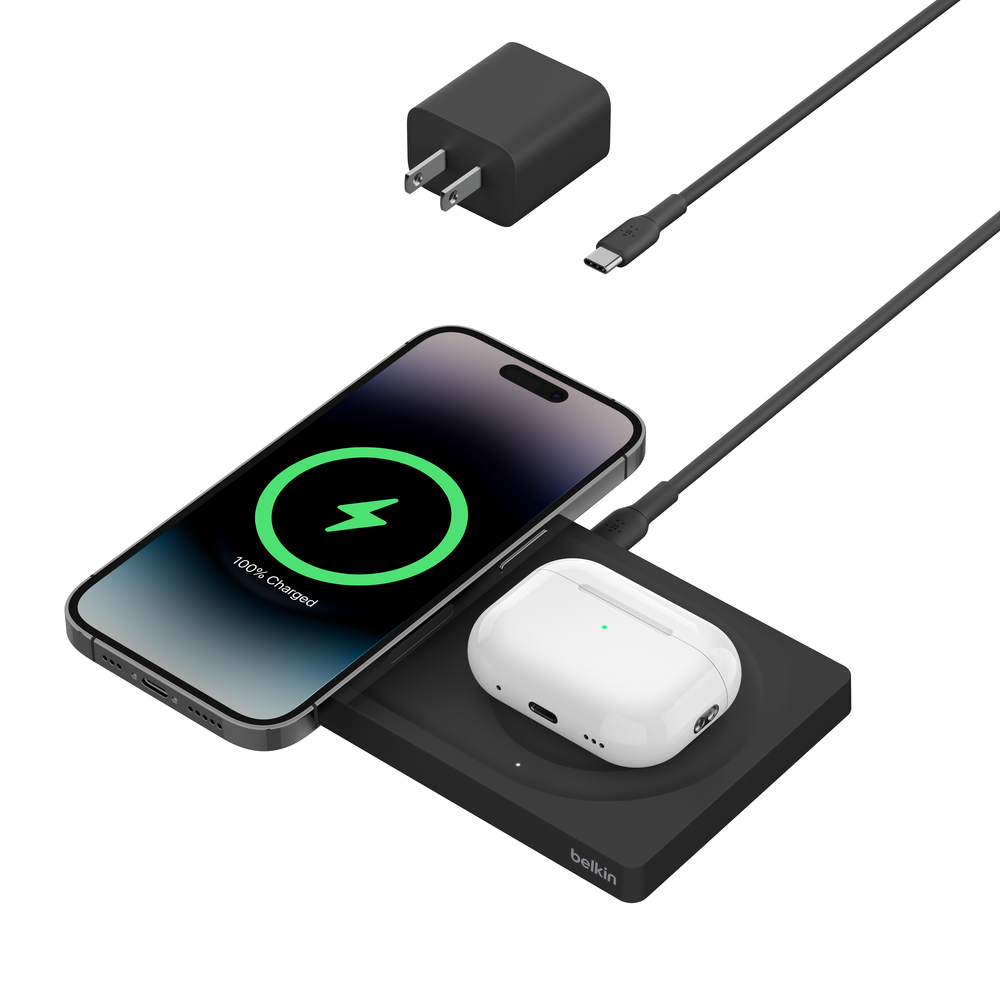
Belkin BoostCharge Pro 2-in-1 Wireless Charging Pad with Official MagSafe Charging 15W, Black
"BOOSTCHARGE PRO 2-IN-1 PAD WITH MAGSAFE BLACK"," | Belkin BoostCharge Pro 2-in-1 Wireless Charging Pad with Official MagSafe Charging 15W, Black
$44.99
$79.99
Price as of November 5, 2026
Give the integration only the operations its current task needs. Where a service cannot express a narrow permission, add a controlled application layer or keep the action manual. The design should not depend on the model remembering to ignore an unnecessary capability.
Treat retrieved material as evidence, not permission
A webpage, document, email, or tool result may contain instructions written by someone other than the user. Such text can be relevant to the requested work without being authorized to redefine it.
OWASP describes indirect prompt injection as malicious instructions entering through external content. Its guidance also notes that retrieval augmentation does not eliminate this class of issue. Read OWASP’s prompt-injection overview. The engineering response is to constrain what can happen when the model follows a bad instruction, rather than assuming every retrieved instruction can be recognized perfectly.
Bind approval to the result that will be used
If a person approves a draft, record which draft and which source they approved. A later article edit or regenerated summary should not inherit approval for a different piece of content. Otherwise an apparently careful review process can publish material the reviewer never saw.
For a publishing workflow, a useful approval record includes the source version, the proposed external text, the destination, and the time of approval. A change to any material part should trigger a new review.
Affiliate pick: workspace accessories
Belkin US
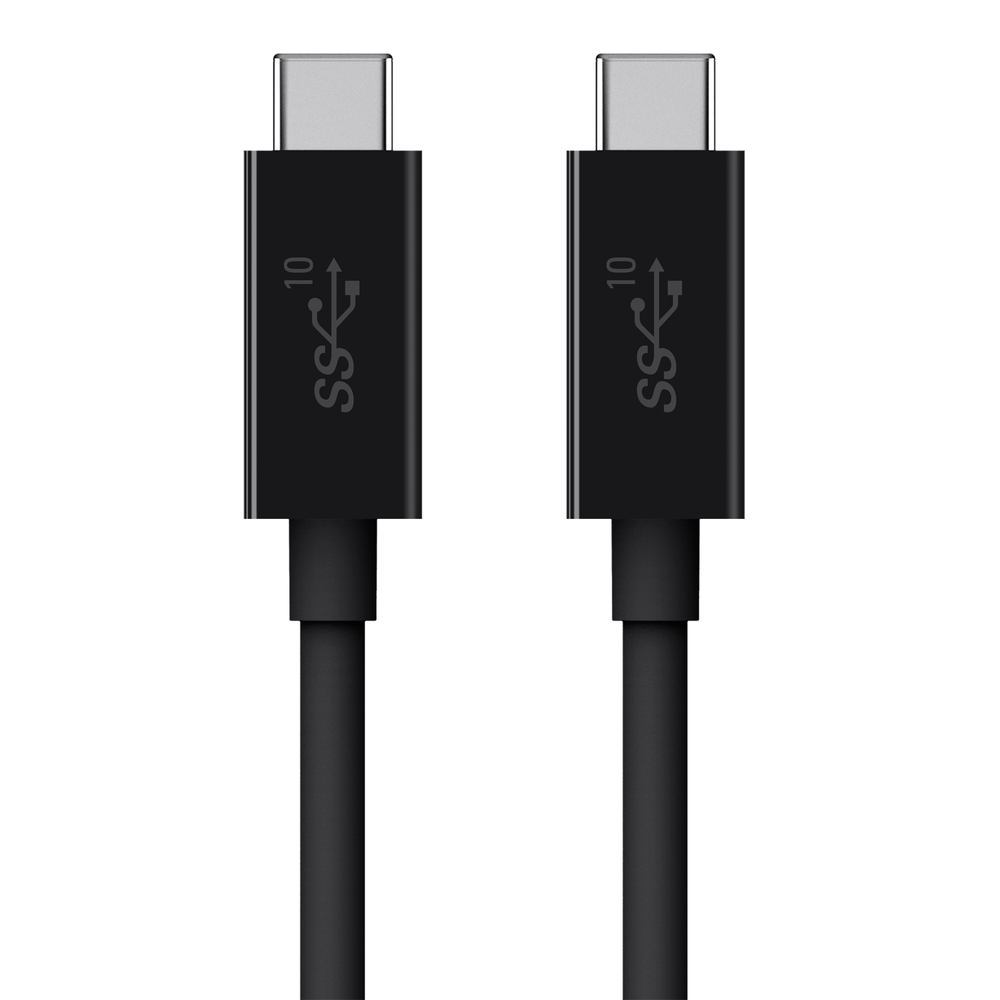
3.1 USB-C to USB-C Data Transfer Charging Cable | Belkin, Black
$(document).ready(function(){ $(\"#usb_c_pencil-banr\").load(\"/resources/static-pages/belkin-usb-c.html #us\");$(\"#usb_c_cable_finder\").load(\"/resources/static-pages/belkin-usb-c_cable_finder.html #us\"); }); THE ULTIMATE USB CONNECTIONThe Belkin 3.1 USB-C to USB-C Data Transfer Charging Cable allows you to experience up to 10 Gbps transfer speeds,…
$24.99
$29.99
Price as of November 5, 2026
Test uncertainty and repetition
A network timeout may mean the external service rejected the operation, or that it accepted it and the reply was lost. Blindly retrying can create duplicates. Decide how the application records an uncertain result and how an operator checks it before another attempt.
- Submit the same task twice and verify duplicate behavior.
- Change the source after approval and verify the approval becomes stale.
- Simulate loss of credentials and confirm the system stops visibly.
- Return malformed or empty output and check that it is not treated as success.
- Put a conflicting instruction inside source material and verify that the application does not expand access.
These are proposed tests. Passing them in one integration does not prove that every prompt-injection attempt or service failure has been covered.
Keep credentials outside the generated content
Store service credentials in an appropriate protected configuration or secret store. Do not place them in prompts, visible drafts, or error messages. Give operators a connection status and a renewal procedure instead of displaying the saved secret.
Logging should answer what was attempted, by which workflow, and with what outcome. It should not collect sensitive material merely because it is available. Redaction needs to cover error paths as well as ordinary success messages.
Make stopping and recovery ordinary operations
Document how to pause the workflow, remove access, inspect a failed task, and resume without replaying completed actions. Someone other than the original implementer should be able to follow that procedure.
NIST’s AI Risk Management Framework provides a broader way to govern and evaluate AI risks. The checklist here is an application design aid, not a claim of NIST certification or complete security assurance.
A trustworthy integration makes its limits visible. It can explain the input, the approved action, the evidence of completion, and the next step when completion is uncertain. That explanation is more useful than describing a system as autonomous without defining what autonomy permits.
Prepared with AI assistance using the linked references and the publishing-system design discussed on Tech Morsels. No independent security audit is claimed. Sources checked October 23, 2026.