
This article contains affiliate links. If you buy through them, MyrinNew.com may earn a commission at no extra cost to you.
🕒 4 min read
Turning off a comment form is not the same as disabling comments. A theme can hide the form while older posts, image attachments, or an API route remain open. The reliable approach is to define the site’s policy, apply it independently of the theme, and test the actual submission routes.
This guide uses a documented MyrinNew.com maintenance case: the default comment setting was open, 436 content records permitted comments or pings, and an unwanted comment was attached to an image. Closing the visible form alone would not have explained or corrected that configuration.
Decide what the site actually needs
First decide whether the policy is “no public discussion anywhere” or “comments on selected articles.” The implementation below concerns the first policy. A site using product reviews, support discussions, or another feature built on WordPress comments needs a more selective design.
Affiliate pick: tech accessories
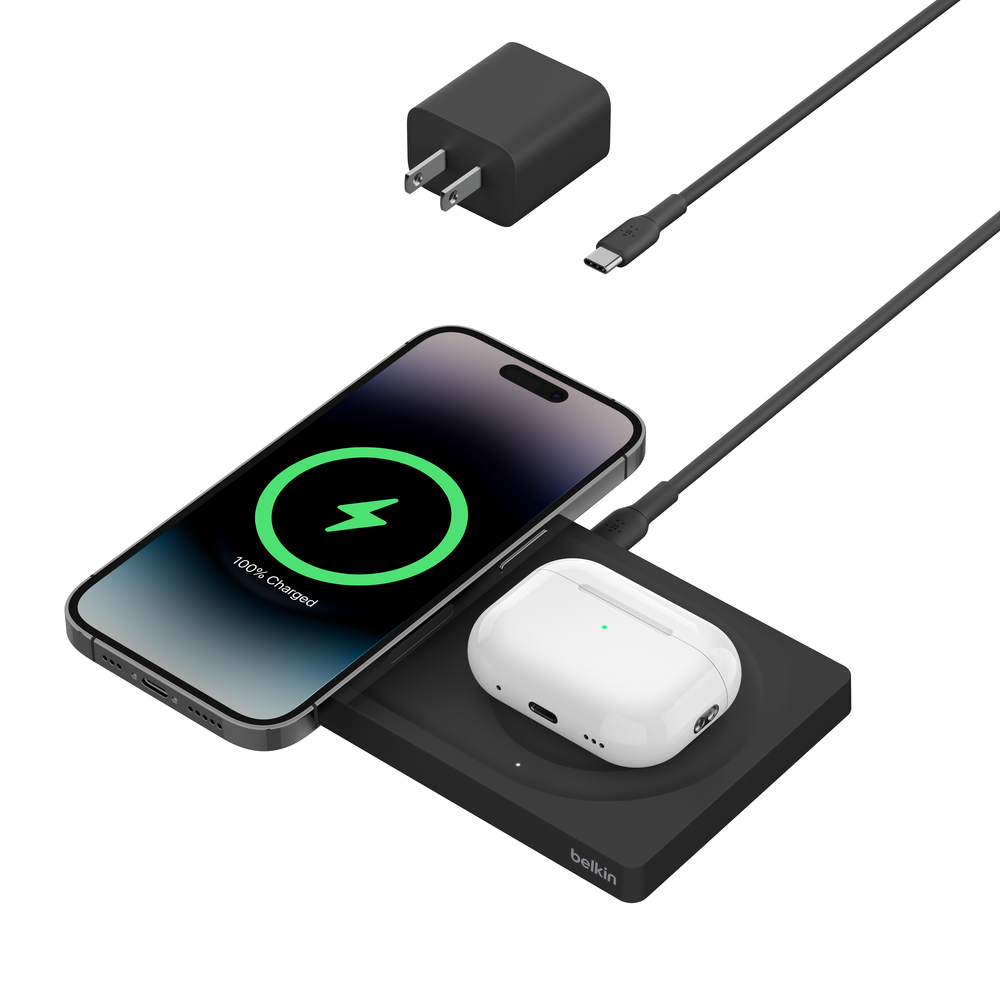
Belkin US
Belkin BoostCharge Pro 2-in-1 Wireless Charging Pad with Official MagSafe Charging 15W, Black
"BOOSTCHARGE PRO 2-IN-1 PAD WITH MAGSAFE BLACK"," | Belkin BoostCharge Pro 2-in-1 Wireless Charging Pad with Official MagSafe Charging 15W, Black
$44.99
$79.99
Price as of October 24, 2026
List the records that can accept discussion: posts, pages, attachments, and public custom post types. Check existing records as well as defaults for new records. Changing a default does not establish the state of material already in the database.
Put the rule where a theme change cannot remove it
A theme’s functions.php is a poor home for a permanent site policy. WordPress supports must-use plugins, loaded automatically from a dedicated directory. They do not have the usual dashboard deactivation control, so they also require a clear maintenance and removal procedure. WordPress documents how must-use plugins work.
For a small site-specific plugin, these filters express the basic runtime policy:
<?php
/** Plugin Name: Site Comment Policy */
defined('ABSPATH') || exit;
add_filter('comments_open', '__return_false', PHP_INT_MAX);
add_filter('pings_open', '__return_false', PHP_INT_MAX);
add_filter('pre_option_default_comment_status', function () {
    return 'closed';
});
add_filter('pre_option_default_ping_status', function () {
    return 'closed';
});
This is the policy layer, not a complete installation script. WordPress’s comments_open filter controls the runtime open/closed result. Existing stored statuses still need to be closed through a backed-up migration, and integrations must be checked separately.
Close existing records without destroying history
Export the affected record IDs and their comment/ping statuses before changing them. Then close those statuses using WordPress APIs. Keeping a reversible record is more useful than a one-off database command with no way to identify what changed.
Affiliate pick: workspace accessories
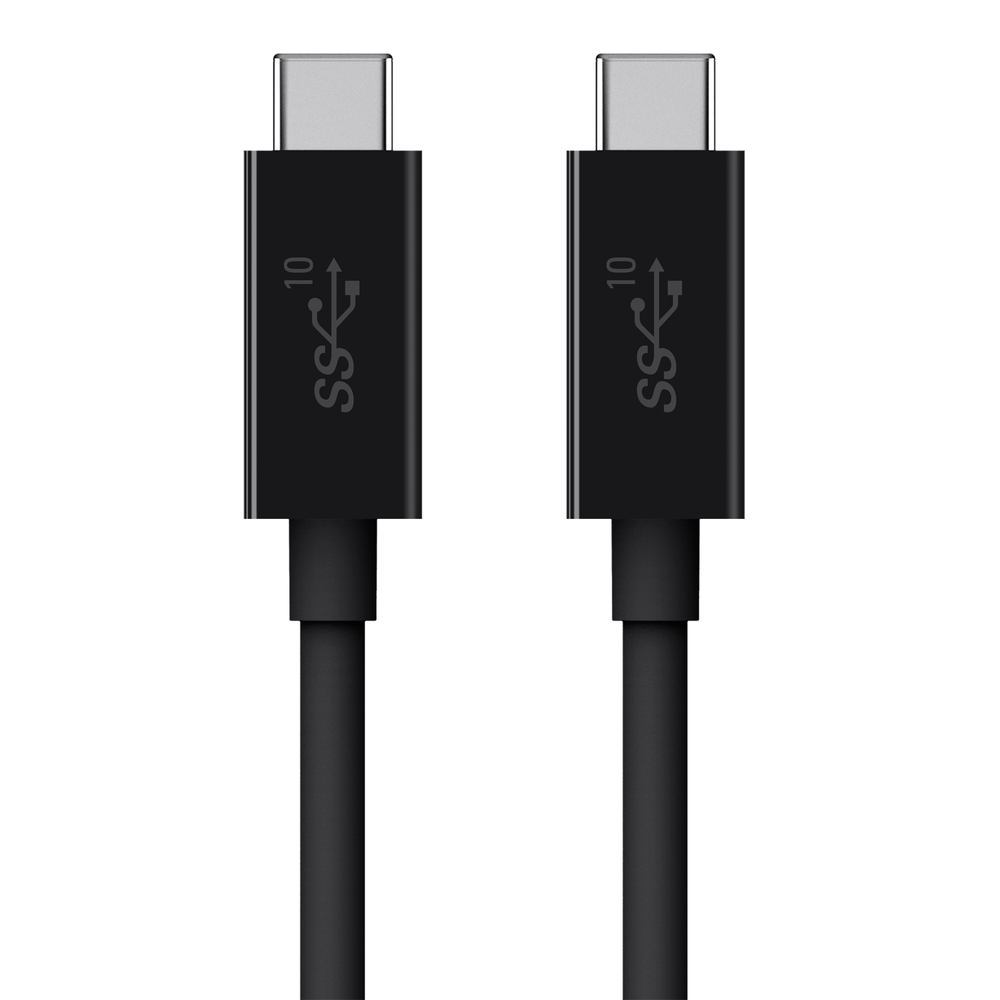
Belkin US
3.1 USB-C to USB-C Data Transfer Charging Cable | Belkin, Black
$(document).ready(function(){ $(\"#usb_c_pencil-banr\").load(\"/resources/static-pages/belkin-usb-c.html #us\");$(\"#usb_c_cable_finder\").load(\"/resources/static-pages/belkin-usb-c_cable_finder.html #us\"); }); THE ULTIMATE USB CONNECTIONThe Belkin 3.1 USB-C to USB-C Data Transfer Charging Cable allows you to experience up to 10 Gbps transfer speeds,…
$24.99
$29.99
Price as of October 24, 2026
Existing comments can be retained, hidden, moderated, or moved to Trash according to the site’s decision. Disabling new submissions does not require permanently deleting legitimate history. In the MyrinNew.com case, the unwanted item was moved to Trash and no permanent deletion was needed.
Check every standard submission path
Test the public comment form handler, REST comment creation, pingbacks, trackbacks, and any comment-related integration. WordPress exposes comment operations through its REST comments interface; hiding a front-end form does not describe that interface’s behavior.
| Check | Evidence from the maintenance case |
|---|---|
| Stored open comment/ping statuses | Reduced from 436 records to zero |
| Public comment and trackback handlers | Test submissions rejected with HTTP 403 |
| Public REST comment creation | Rejected; application-level test also returned 403 |
| XML-RPC comment/pingback methods | Removed from the registered method list |
| Test comment records | No new test comments created |
| Ordinary homepage | Still returned HTTP 200 |
Record the response and inspect the comment count after each test. A rejection page is useful evidence; confirming that no record was created is stronger. Use a harmless test message and avoid publishing test material to readers.
Know the boundary of the result
The checks establish that the tested standard routes were closed under that configuration. They do not prove that an unrelated plugin cannot write directly to the database or that a compromised administrator account cannot change the site. A custom integration can create its own endpoint and must be assessed on its own terms.
Nor does a closed endpoint stop network requests from arriving. Bots may continue sending traffic. The operational goal is to reject unwanted submissions consistently while preserving the pages and features the site actually uses.
A maintenance checklist worth keeping
- Keep the policy plugin and a rollback copy under change control.
- Check a post, a page, and an attachment after theme or discussion-related plugin changes.
- Verify that new content inherits the closed policy.
- Monitor rejected requests and unexpected comment records separately.
- Retest custom forms and integrations when they change.
The broader lesson is useful beyond WordPress: define the rule at the application boundary, apply it to historical state, and verify the resulting behavior. A missing button is a presentation choice. A rejected write is a control.
Implementation case reviewed October 23, 2026. This article was prepared with AI assistance using the documented site changes and linked WordPress references; it does not claim to be an independent penetration test.